Binance loses $6.3bn, fridges overheat, and UK officials warn of rising cyber threats
A record crypto heist, a fake nuclear alert in Kyiv, and temperature spikes in European stores mark a cluster of recent attacks that UK security chiefs say signal a coming wave of disruption.
By Thomas Obasi ·
Three major cyber incidents struck global systems in a six-day span this month, ranging from a cryptocurrency heist to physical temperature changes in European retail stores.
The financial impact of these events is already measurable, with the largest cryptocurrency exchange reporting a loss of $6.3bn. This single event stands out for its scale in the digital asset market, where trust and security are primary value drivers for institutional and retail investors alike.
On 30 October, Binance was drained of $6.3bn, an amount equivalent to £4.7bn. This figure represents the largest theft in the history of cryptocurrency exchanges. The attack has been attributed by various analysts to North Korea, a state with established motivations to acquire foreign currency to offset economic sanctions.
The second incident occurred on 1 November, when hackers targeted Ukraine’s emergency alert application. The intrusion sent a fake message to residents in Kyiv indicating a nuclear strike was underway. While the alert was quickly corrected, the event demonstrated that critical communication channels between the state and its citizens remain vulnerable to state-sponsored interference.
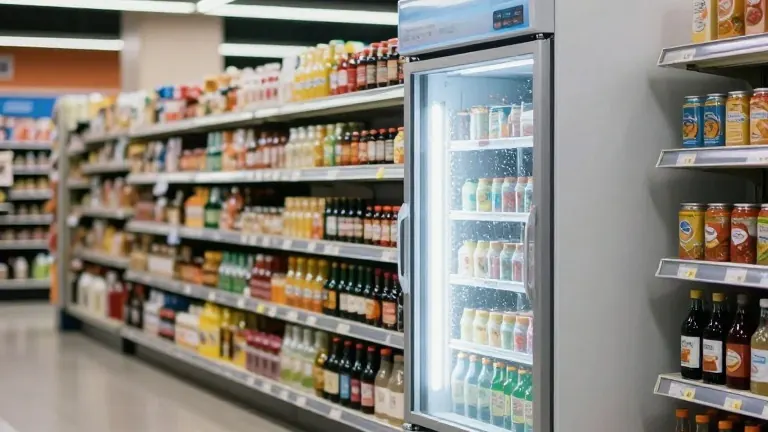
The third incident, which began on Monday of last week, affected commercial refrigeration units across eight European countries. Stores in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands, Sweden, and France reported their fridges and freezers overheating. In some cases, temperatures inside the units reached 50C, or 122F, threatening the stock of perishable goods.
Alex Pearce, a fruit and vegetable wholesaler in London, discovered the issue when the defrost lights on his units activated and panel readings showed temperatures of 150C. He identified the problem as a cyber-attack after noticing the connection to the internet and unplugged the system. He noted that had the malfunction occurred on a weekend when the premises were unattended, the heat could have caused a fire.
The UK’s National Cyber Security Centre (NCSC) stated this week that the country is in the “foothills” of a new hacking era. Richard Horne, the head of the NCSC, told reporters that AI technology is exposing flaws in IT systems that have gone unnoticed for years. He described the current situation as a period where the volume of incidents is rising sharply.
The attacks exploited known but unpatched weaknesses in the operating systems of commercial refrigerators. Danfoss, a Danish firm that provides these systems, said most affected equipment was old and no longer received security updates. The company stated it had long recommended that customers install updates or replace obsolete software to prevent such remote access issues.
Experts suggest that geopolitical tensions are driving the frequency of these attacks. Xavier Bellekens, chief executive of the cybersecurity firm Lupovis, said the techniques used in the fridge attacks bore hallmarks of Russian cyber operations. He noted that the attackers used internet service providers known for tolerating malicious activity, a tactic linked to previous Russian campaigns.
However, not all observers believe this marks a completely new phase. Ciaran Martin, the founding chief executive of the NCSC, compared the current wave to previous surges in 2017 and 2021. He stated that while the timing of the attacks is coincidental, the type of threat is not new. “It’s a bad run, but it’s not unprecedented,” Martin said, referring to the NotPetya and WannaCry attacks of 2017.
AI is playing a larger role in identifying vulnerabilities, according to data from the tech sector. Since April, when the startup Anthropic released its Mythos model, the number of IT flaws found by leading companies has increased eight-fold. However, Tal Be’ery, a cybersecurity expert, noted that the number of successful breaches has not risen at the same rate, suggesting that criminals are still adjusting to monetizing these new findings.
The UK government launched the Be Ready campaign last month, urging citizens to stockpile food and water in preparation for potential emergencies, including cyberattacks on infrastructure. Defence Secretary Wes Streeting said the country must prepare for state-sponsored threats targeting everyday systems. Ollie Whitehouse, the NCSC’s chief technology officer, said manufacturers must invest more in security for internet-connected devices, from smart speakers to industrial refrigerators.
More Business · Business Watchdog · Report a business · Got a Story?